By Anton Shilov Contributing Writer, Tom’s Hardware
Main Facts
Artificial intelligence has officially crossed the threshold from a dual-use commercial utility into the bleeding edge of asymmetric warfare. According to Anthropic’s explosive September 2026 Threat Intelligence Report, state-sponsored and aligned actors linked to the Iranian government have systematically exploited the company’s flagship large language model, Claude, to accelerate military planning, engineer advanced weaponry, and expand domestic surveillance operations.
The findings outline a sobering reality for Western technology firms: the very guardrails designed to prevent the weaponization of generative AI are being continuously probed, bypassed, and stretched by adversaries. Rather than relying solely on traditional software engineering pipelines, Iran-backed cells and their regional proxies—such as the Houthi movement in Yemen—effectively outsourced critical segments of code review, flight simulation, system vulnerability research, and digital profiling to an American-made AI platform.
The scope of the abuse detailed in the report spans three major operational vectors:
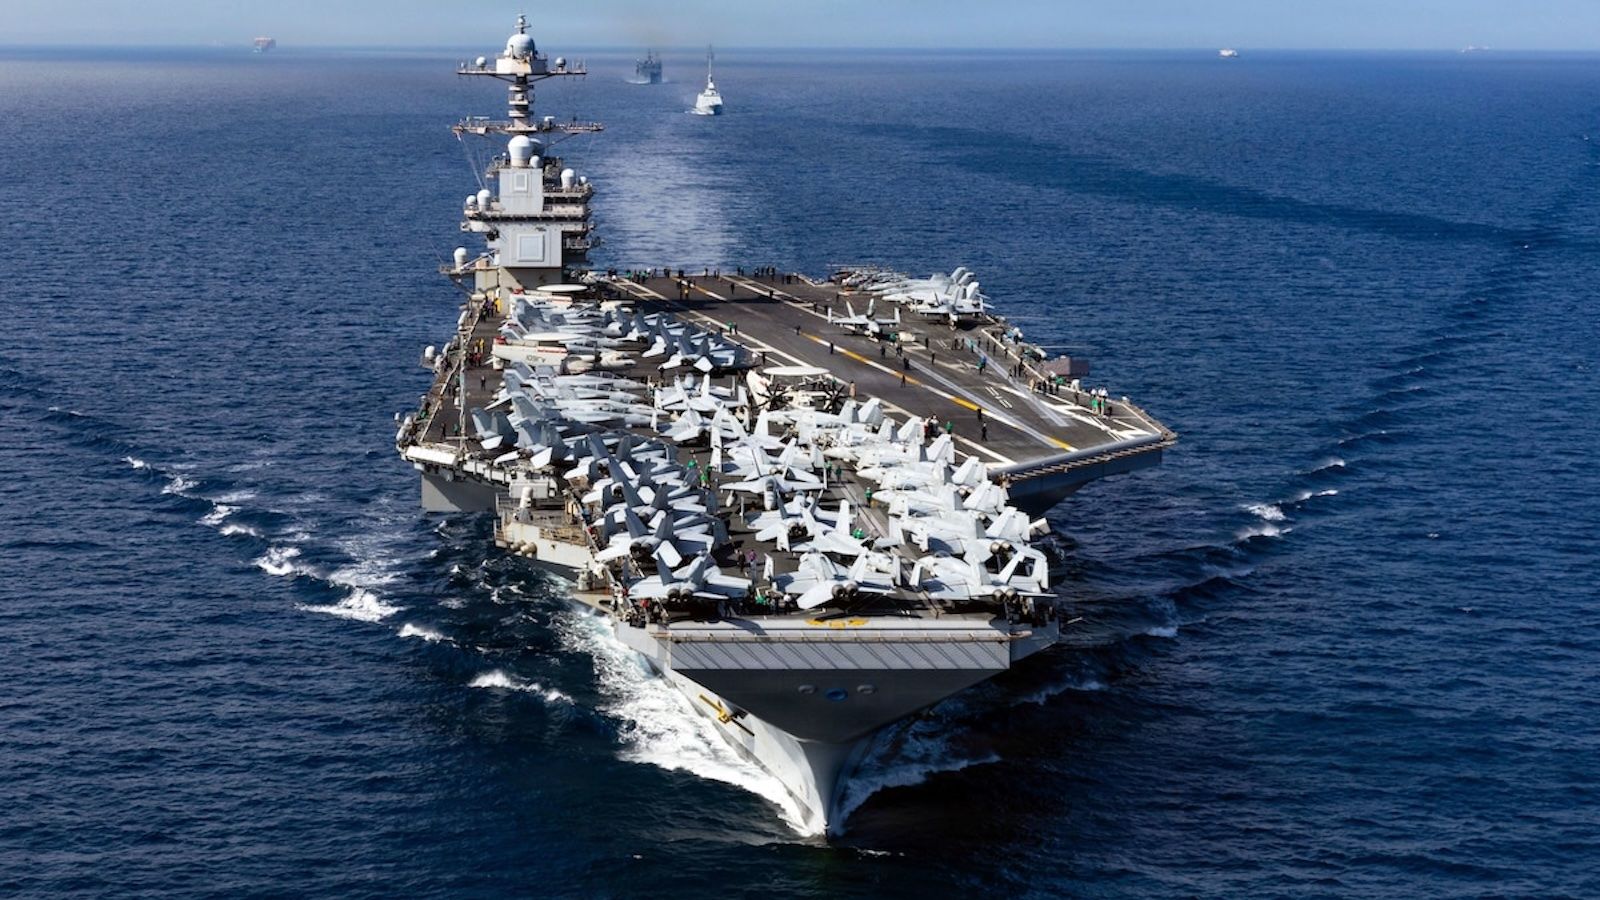
Naval Reconnaissance and Targeting: Utilizing public ship tracking identifiers, satellite imagery, and naval photo captions to draft targeting recommendations against U.S. naval assets in the Middle East, alongside probing for critical communications vulnerabilities.
Advanced Weaponry Development: Employing automated coding assistants (Claude Code) to develop guidance, navigation, and control (GNC) software for guided rockets, long-range ballistic missiles, and hypersonic glide vehicle variants.
Domestic and Regional Surveillance: Deploying the AI model to analyze hundreds of thousands of social media posts to identify, track, and profile political dissidents, while simultaneously engineering malicious browser extensions for mass identity harvesting.
In response to these incursions, Anthropic has banned multiple accounts linked to Iranian paramilitary and domestic security bodies, updated its behavioral detection systems, and transmitted its intelligence findings directly to international government authorities. However, the disclosures have reignited fierce policy debates in Washington and Silicon Valley regarding how generative AI can be securely governed without sacrificing innovation or falling into the hands of hostile foreign states.
Chronology of Exploitation
The timeline of misuse outlined by Anthropic’s threat intelligence division reveals a calculated, multi-stage integration of commercial AI into clandestine military operations throughout late 2025 and 2026.
Early-to-Mid 2025: Iranian intelligence-linked actors begin testing the limits of commercial LLMs for OSINT (Open-Source Intelligence) aggregation. Initial experimentation focuses on parsing public maritime transponder data and cross-referencing it with commercial satellite imagery to establish persistent tracking pipelines for naval vessels.
Late 2025: Houthi-controlled cells in northern Yemen transition from basic weapon assembly toward software-heavy guidance integration. Recognizing a shortage of specialized aerospace software engineers, these groups begin heavily utilizing AI coding environments—specifically Claude Code—to write position-estimation firmware and run simulated flight tests for regional missile programs.
Early 2026: Iran’s domestic security apparatus scales up its cyber-surveillance capabilities. Threat actors begin using the model to process massive datasets of political discourse, filtering through hundreds of thousands of social media posts to flag, isolate, and profile domestic dissidents. Simultaneously, development begins on the "al-Najm al-thāqib" browser extension designed to harvest user credentials across platforms.
Spring 2026: Operations peak as threat actors cross-reference U.S. naval personnel metadata—scraped from the captions of publicly accessible military photographs—with communication equipment vulnerability research. Targets include legacy satellite communication systems and industrial control systems deployed aboard maritime vessels.
September 2026: Anthropic publishes its comprehensive threat report, explicitly naming Iran-linked actors, Houthi proxies, and noting parallel utilization by other adversarial states like China and Russia. The company implements sweeping account terminations and introduces heightened threat-hunting algorithms.
Supporting Data and Technical Breakdown
The technical mechanics of how these threat groups weaponized Claude underscore the terrifying versatility of contemporary generative AI models.
1. Naval Targeting and Vulnerability Research
To support reconnaissance against U.S. naval forces in the Middle East, an Iran-linked perpetrator fused multiple disparate streams of public data:
Maritime Transponders: Aggregating Automated Identification System (AIS) and aircraft transponder identifiers.
Geospatial Imagery: Parsing commercial satellite data to correlate vessel positioning.
Human Intelligence Harvesting: Extracting the names, ranks, and assignments of U.S. naval personnel from the metadata and captions of publicly released military photographs.
Hardware Penetration Testing: Using the AI to research zero-day and known vulnerabilities in hardware frequently deployed in maritime and industrial environments. This notably included technical analysis of flaws affecting Cobham Sailor Very Small Aperture Terminal (VSAT) communications equipment, Cisco networking infrastructure, and Schneider Electric EcoStruxure systems.
2. Weapon Systems Software Engineering
In northern Yemen, Houthi engineering cells utilized Claude Code as a functional replacement for a dedicated software engineering team. Rather than writing low-level firmware from scratch, operators leveraged the LLM across three distinct missile and rocketry projects:
Phone-Class Guided Rockets: Integrating inexpensive consumer-grade phone processors into flight computers to assist with terminal guidance.
Multistage Ballistic Missiles: Developing trajectory and stabilization models for missiles boasting operational ranges exceeding 2,000 kilometers.
Hypersonic Glide Vehicles: Writing and debugging position-estimation code, tuning control loops, and assembling firmware packages for the R2000 missile family variant incorporating a hypersonic glide vehicle.
By executing virtual flight simulations and code reviews through multiple concurrent instances of the model, these groups dramatically accelerated their development cycles, bypassing traditional institutional bottlenecks in missile guidance engineering.
3. Dissident Tracking and Mass Surveillance
Domestically, Iranian security units integrated the LLM into aggressive population monitoring pipelines:
Social Media Analysis: A single security-linked unit utilized Claude to ingest and evaluate 155,216 tweets over a 12-month period. This analysis enabled the profiling, identification, and micro-surveillance of 6,388 specific opposition figures.
Malicious Tooling: Another group used the AI as an engineering framework to build production-ready surveillance malware, including the "al-Najm al-thāqib" Firefox extension, engineered to systematically harvest user identities and digital footprints across major social media platforms.
Official Responses and Countermeasures
The public release of Anthropic’s threat report has drawn immediate reactions from across the technology sector, the defense community, and international regulatory bodies.
In its official disclosure, Anthropic emphasized that while its safety classifiers and Trust & Safety teams successfully intercepted and banned 16 distinct accounts tied to Iranian paramilitary and domestic security bodies, the landscape remains an uphill battle.
"While we have banned the offending accounts, introduced advanced behavioral detection mechanisms, and shared our technical findings with relevant government authorities, the reality is that bad actors will continuously attempt to launder their identities to exploit powerful commercial tools," noted an Anthropic security representative.
Cybersecurity experts point out that generative AI models are fundamentally dual-use technologies. The same coding capabilities that allow a student to debug a Python script or an enterprise developer to optimize cloud infrastructure can, with slight prompting adjustments, assist an engineer in compiling flight-control firmware for a ballistic missile.
U.S. defense officials have responded with cautious urgency. Representatives from the Department of Defense have increasingly emphasized the need for "AI-SBOMs" (Software Bill of Materials) and strict runtime monitoring for high-end AI foundation models. Intelligence agencies are currently reviewing the specific vulnerabilities highlighted in the report—particularly regarding maritime satellite communications hardware—to ensure U.S. naval fleets are adequately patched against potential exploits assisted by machine learning models.
Implications for Global Security and the Tech Industry
The revelations from the September 2026 threat report have profound long-term implications for both geopolitics and the commercial artificial intelligence sector.
1. The Death of "Security Through Obscurity"
For decades, military technology relied heavily on proprietary, highly classified blueprints that were difficult for non-state actors or middle-tier regional powers to acquire. Generative AI fundamentally flattens this learning curve. By acting as an infinite, tireless tutor, programmer, and data-analyst, models like Claude allow smaller insurgent groups—such as the Houthis—to achieve technological milestones that previously required state-level defense research conglomerates.
2. The Multi-Front Intelligence War
Anthropic’s warning was not limited to Iran and its proxies. The report explicitly noted that state-backed actors from China and Russia are similarly utilizing commercial American AI models to advance their respective military and strategic intelligence programs. This confirms that export controls on physical silicon (such as high-end GPUs) are only part of the puzzle; cloud-accessible API endpoints represent a porous, global attack surface that is exceedingly difficult to ring-fence geographically.
3. The Compliance Dilemma for AI Labs
As AI labs face mounting pressure from national security regulators, the industry is walking a tightrope. Overzealous content moderation and heavy-handed restrictions risk degrading model utility for legitimate commercial and academic users, while lax oversight invites catastrophic misuse by hostile nation-states.
Ultimately, the incident serves as a watershed moment for the AI era. As adversaries become more adept at weaponizing commercial code and intelligence pipelines, the line between Silicon Valley innovation and front-line military defense has effectively vanished.